Protection at network level
Works on the traffic for a customer's IP ranges, so mail servers, VPNs, remote access and every other service behind the line are covered, not only the website.
Protects a customer's entire Dedicated Internet Access line, not just one website. Traffic for their IP blocks is routed through the Network Threat Shield and cleaned before it reaches the line, so every server behind it is protected.
Works on the traffic for a customer's IP ranges, so mail servers, VPNs, remote access and every other service behind the line are covered, not only the website.
Start by watching what would be dropped on the customer's real traffic, then switch to Enforce when the policy is right.
Run as a routed hop for the customer's prefixes, or inline at layer 2 in front of the line, depending on how your network is built.
Deployed, monitored and moved from ORMIZ GUARD alongside every other node, with live health and uplink bandwidth on the radar.
The same pipeline protects a single website or an entire internet line. Switch between them, and between watching and blocking.
The website's DNS points to the ORMIZ AI Threat Shield node, so every request for the site arrives there first.
Each request passes five checks: network, fingerprint, behaviour, AI intent and policy. In Enforce mode, attacks are blocked or challenged.
Only clean traffic is passed on to the customer's web server. The site's dashboard shows what was stopped.
ORMIZ Network Threat Shield cleans all traffic for a customer's IP blocks before it reaches their Dedicated Internet Access line. Run it on a virtual machine or on dedicated hardware.
ORMIZ GUARD deploys the Network Threat Shield onto a virtual machine and manages it alongside every other node in the fleet.
Run the Network Threat Shield on a dedicated server. Deploy it from ORMIZ GUARD, or install it directly on the machine with the standalone installer.
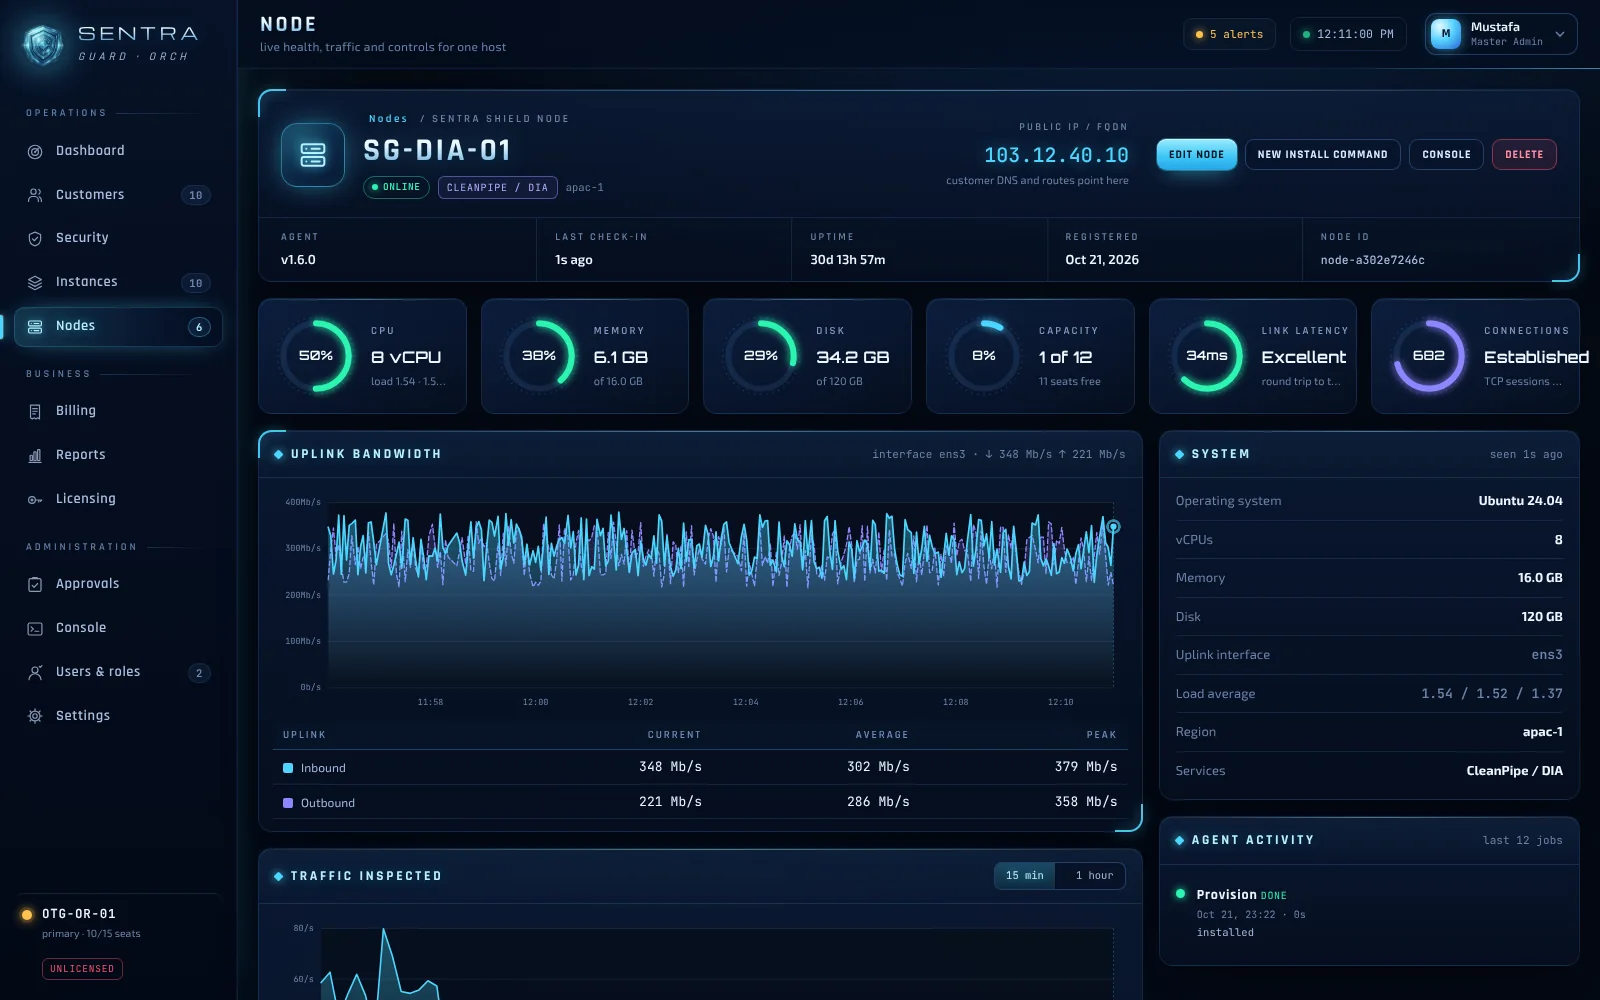
These are the real ORMIZ consoles. The figures shown are demo data.
Live health, uplink bandwidth and traffic inspected for a single shield node, with the controls to manage it.
Book a walkthrough, or start with a free Safety Check of your site.